Security
Encryption, compliance, and threat analysis from the team building split-key file exchange.

Block Sending to Freemail and Disposable Email Domains
Prevent unauthorized sharing by restricting sending files to freemail and disposable email domains.

Podcast Recap: Reducing the Cybersecurity Blast Radius
Learn how to minimize the impact of data breaches by managing sensitive information and using SendSafely to enhance security in your workflows.

ServiceNow Patched Three Max-Severity Flaws. What's Sitting Inside Your Instance Didn't Change.
Protect your sensitive customer data with SendSafely Halo for ServiceNow, ensuring files remain encrypted and outside your instance amid recent vulnerabilities.

ServiceNow's Latest Security Incident: Unauthenticated Remote Sandbox Escape & How SendSafely Halo Protects Your Customer Data
Learn how SendSafely’s Halo integration enhances security in ServiceNow, protecting sensitive customer data against vulnerabilities like CVE-2026-6875.

Your AI Doesn't Need a Zero-Day. It Already Has the Credentials.
Discover how AI can exploit credentials rather than zero-day vulnerabilities, and learn how SendSafely Halo protects sensitive data in support interactions.

Shut Everything Down: The ShareFile Wake-Up Call
Progress Software's decisive response to a security threat highlights the risks of complex file-sharing architectures. Learn how end-to-end encryption can mitigate these vulnerabilities.

When Helpful AI Gets Hijacked: Reducing the Blast Radius with SendSafely HALO
Learn how SendSafely HALO minimizes risks of AI hijacking by controlling data access, ensuring sensitive information remains secure in customer interactions.

Debug Files (aka. The HAR File Problem): Why Your Support Process Is a Liability to Your Customers' Security
Prevent your company support workflows from quietly leaking your customers' credentials.

You Can't Have True Sovereign AI Without Sovereign Data
Protect your company's data and maintain sovereignty in AI. Discover how SendSafely Halo secures your sensitive information before it reaches AI models.

What ServiceNow Teaches Us About Blast Radius
The ServiceNow incident disclosed in June 2026 is a reminder that the agent isn't the only thing that can fail.

Salesforce Is Back in the Crosshairs: Why Blast Radius Matters
Blast radius: when a trusted integration is compromised, how much of your sensitive data is sitting there to be taken?

SendSafely the Enterprise AI Trust Layer
In our recent post on vibe coding platforms, we covered the growing security risks in the AI stack.

IP Restrictions: Lock Down Access to Your SendSafely Portal
Security teams spend a lot of time hardening credentials, but stolen credentials are still one of the most common ways attackers get in.

Vibe Coding Security
Vibe coding platforms are changing how software gets built. But recent AI security headlines is a timely reminder: speed and convenience don’t come with a security guarantee.

Your Customers' Sensitive PII Shouldn't Be Training Someone Else's AI

Security spotlight: How we use Burp DAST at SendSafely
This post is part of our ongoing monthly series where we highlight the enterprise security tools we use internally and explain how they help us build secure software.
New Event Trigger: Add Recipient
SendSafely Actions just got more flexible. We’ve introduced a new event that triggers when a recipient is added to a transfer package or workspace.

Security Spotlight: How we use Socket at SendSafely

Using Security Groups to Restrict Outbound Sending
SendSafely has launched a new Security Group permission that limits access to sending outbound files.

Security Groups: Fine-Grained Control Over SendSafely Permissions
Managing permissions across a growing user base can be challenging, especially when different teams require different levels of access to sensitive features.

Securing Customer Data with SendSafely: A Guide for BPO Operations

SendSafely & AI: Building secure data exchange into your AI deployments
Deploying AI tools should be exciting, not anxiety-inducing.

Sunsetting Legacy Subscriptions: What You Need to Know
At SendSafely, we’re committed to delivering the best security, performance, and support to our customers.

Automate fast with our pre-built Actions Library
SendSafely's new library of pre-built Actions templates fast-tracks the process of getting your workflow in place.

Guest Authentication using an IdP (Single Sign-on)
You can now leverage your own external identity provider \(IdP\) to authenticate your SendSafely guests via single sign-on.

SendSafely Audit Log API
SendSafely's new Audit Log API provides security and compliance teams broader visibility into events occurring in the SendSafely platform.

Data Privacy: Isolated Geographic Hosting
With the increased focus on data privacy and security worldwide, many countries now regulate the use and protection of personal data through federal and state laws.

Protecting Customer Data with Automatic File Expiration and Deletion

SendSafely and GDPR
The General Data Protection Regulation \(GDPR\) imposes certain requirements for companies that collect, store, or process personal data of European Union residents.

Securing Customer PII with Remote Service Desk Agents

SendSafely: Secure Communications Solution of the Year
We are proud to announce that SendSafely's Serverless Email Gateway \(SEG\) has been named Secure Communications Solution of the Year in the fifth annual CyberSecurity Breakthrough Awards.

COVID-19 Vaccine Contest: A Case Study

SendSafely Workspaces: Secure Enterprise Collaboration
With all the recent high profile hacks occurring across the globe it is becoming readily apparent that encrypting data in transit is no longer enough.
Using Content Security Policy to Prevent Cross-Site Scripting (XSS)
On SendSafely.com we make heavy use of many new JavaScript APIs introduced with HTML5. We encrypt files, calculate checksums and upload data using pure JavaScript.

Building a Custom Web Form with End-to-End Encryption
If you need to collect sensitive data from customers, like social security numbers or credit card information, using a web form can be an attractive option.

4 Tips to Help You Stay Prepared for a HIPAA Audit
If you work in the healthcare field, you’re probably somewhat familiar with the Health Insurance Portability & Accountability Act \(commonly known as HIPAA\).

Encryption Tips for CPAs and Tax Professionals
It’s that time of the year again, tax season. Un-arguably the most hectic time of the year for any CPA or tax professional.

Does Your Law Firm Need Email Encryption?
The practice of law is constantly evolving. As with most businesses, email has become the most common method for exchanging information with clients.

Reasons why your business needs a secure FTP alternative
The File Transfer Protocol \(FTP\) has been around for a very long time.

5 Quick Tips for Handling TILA RESPA Integrated Disclosure Changes and Compliance with ALTA Guidelines
Security and privacy are popular topics these days.
Slides from OWASP AppSec USA

AppSec USA 2013 in NYC!
Next week SendSafely will be at the 2013 OWASP AppSec USA conference, right here in New York City.
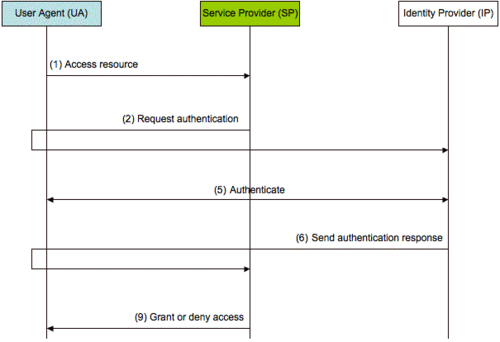
Web-based Single Sign-On and the Dangers of SAML XML Parsing
Security Assertion Markup Language \(SAML\) is a popular XML-based open standard for exchanging authentication and authorization data between two systems.

Notes about Chrome v40 and Content Security Policy Level 2
Here at SendSafely, we’ve advocated the use of Content Security Policy and have been running a fairly strict CSP in block mode for over a year now.
Hello World
Hi Everyone\! Today marks the official launch of the SendSafely Blog.

Bypassing Content Security Policy with Java Applets
SendSafely Featured on Twilio Blog
Our friends at Twilio have written up an article on their blog about how we use their API to provide strong authentication for our users.
Retrofitting Code for Content Security Policy
Update: Google notified us that they re-factored the reCAPTCHA JavaScript code to be CSP friendly.
Come say “Hi” at AppSec EU!
We are sharing a booth with our sister company, Gotham Digital Science, at this year’s AppSec EU conference in Cambridge.