
This post is part of our ongoing monthly series where we highlight the enterprise security tools we use internally and explain how they help us build secure software.
__Here at SendSafely, we make heavy use ofBurp Suite DAST by PortSwigger to continuously scan our application perimeter for vulnerabilities. Our security team has used Burp Suite tooling for years in previous roles as application security specialists and red team penetration testing professionals, so adopting Burp DAST as our enterprise scanning platform was a natural extension of tooling we already knew and trusted.
Dynamic Application Security Testing (DAST) is the practice of probing a running application from the outside, the same way an attacker would. Unlike static analysis tools that examine source code, DAST sends real payloads to real endpoints and evaluates how the application responds. This “black box” approach is essential for catching the kinds of runtime vulnerabilities that only become visible when an application is actually running: authentication bypasses, injection flaws, insecure direct object references, and more.
For a security-first platform like SendSafely, maintaining a secure application perimeter isn’t optional. It’s fundamental to everything we do.
Why Burp DAST makes sense for SendSafely
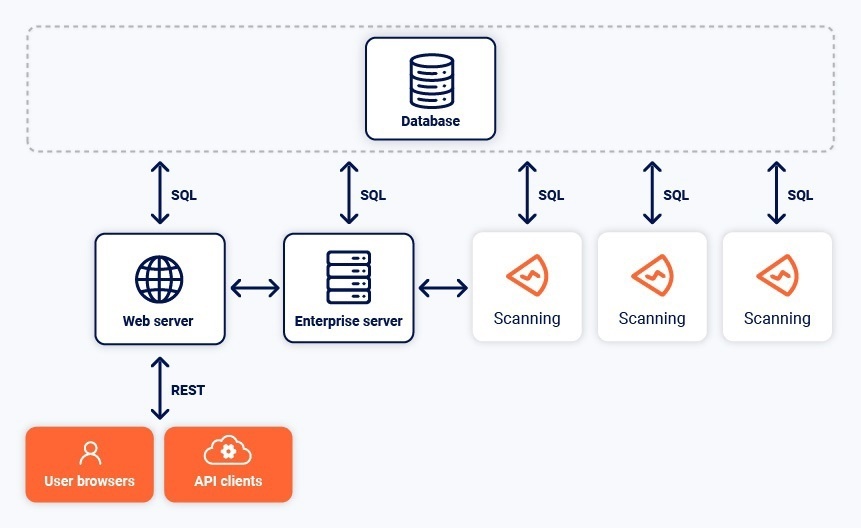
The security tools we adopt need to meet a high bar: they should be accurate, automatable, and tightly integrated with the way we already work. Burp DAST checks all three boxes. The scanning engine is trusted by over 17,000 organizations worldwide, and the enterprise platform wraps that engine in the operational features (scheduling, integrations, reporting, compliance) that make it practical to deploy at scale.
A shared baseline that builds trust and efficiency
Burp Scanner is ubiquitous enough in the security industry that its findings represent a common shared context. When we share results with security teams at our enterprise customers, whether during vendor reviews, penetration testing engagements, or compliance assessments, there’s an immediate understanding of the tool, what the findings mean, and how they were scored. That common ground removes friction and accelerates trust.
Internally, it also lets our security team use the scan results as a reliable baseline, freeing them to focus on higher-specialty testing specific to our platform’s architecture and threat model rather than re-litigating standard vulnerability classes.
Automation and regular scanning: “always-occurring” analysis
One of the most valuable aspects of Burp DAST is how easily it lends itself to automation. Rather than treating vulnerability scanning as a periodic, manual event, we use Burp DAST to run scheduled scans on a daily and weekly basis across our application portfolio. This ensures that our security reports are always current and that newly introduced changes are evaluated quickly, not weeks later when the context has been forgotten.
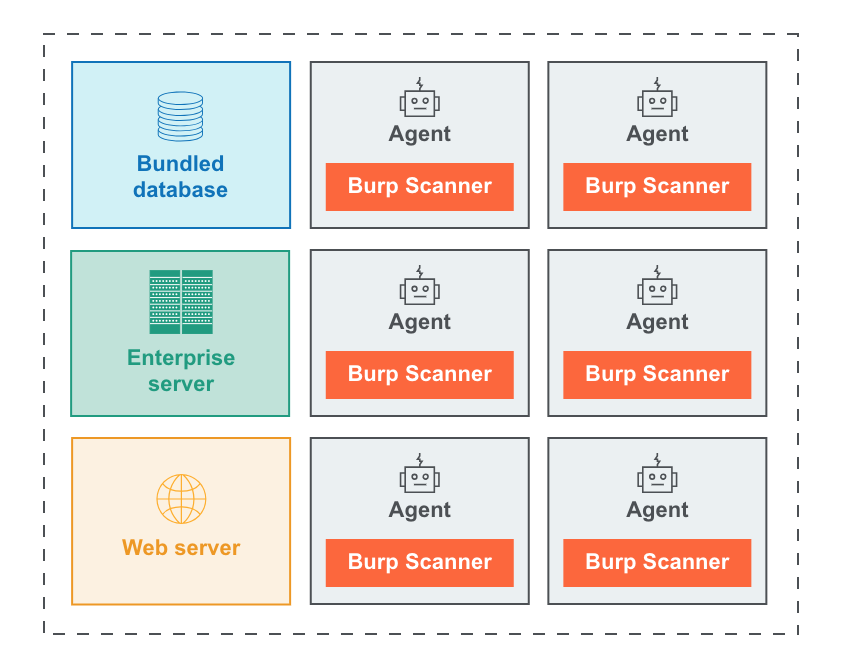
Automated scanning also removes the dependency on any single team member to remember to “run the scan.” The schedule runs regardless of sprint cycles, on-call rotations, or competing priorities. Because Burp DAST supports both unauthenticated and authenticated scanning, it provides visibility across our entire attack surface with a layered view of exposure from the outside in.
For a security team, that kind of always-on coverage is invaluable. We can focus our attention on remediating findings rather than orchestrating the scanning process itself.
High accuracy findings: Less noise, more signal
Alert fatigue is a real problem in application security. When a scanner floods your team with low-quality findings, the truly critical issues can get lost in the noise, or worse, the team starts tuning everything out.
Burp Scanner is purpose-built to maximize detection accuracy while minimizing false positives. A key feature is automated Out-of-Band Application Security Testing (OAST), a technique pioneered by PortSwigger that identifies subtle, asynchronous issues like blind SQL injection and server-side request forgery (SSRF) with a very high degree of confidence.
In practice, this means our team spends less time chasing phantom vulnerabilities and more time fixing real ones,
What’s next
Burp DAST is one of several enterprise security tools that form the backbone of our application security program. In upcoming posts in this series, we’ll continue highlighting the tools and practices that help us deliver on our security commitments to customers.
If you’re interested in how we think about security at SendSafely, stay tuned, and feel free to reach out.
SendSafely: Integrated File Transfer for the Apps you Love
If you are looking for a secure way to send or receive files with anyone, or simply need a better way to transfer large files, our platform might be right for you.
Request a Demo


