#AppSec
Everything on the SendSafely blog tagged AppSec.

HALO: The Trust Layer Your AI Is Missing
AI is being wired directly into your business: your CRM, your support tools, your internal systems.

Vibe Coding Security
Vibe coding platforms are changing how software gets built. But recent AI security headlines is a timely reminder: speed and convenience don’t come with a security guarantee.

Security spotlight: How we use Burp DAST at SendSafely
This post is part of our ongoing monthly series where we highlight the enterprise security tools we use internally and explain how they help us build secure software.

Security Spotlight: How we use Socket at SendSafely
Using Content Security Policy to Prevent Cross-Site Scripting (XSS)
On SendSafely.com we make heavy use of many new JavaScript APIs introduced with HTML5. We encrypt files, calculate checksums and upload data using pure JavaScript.
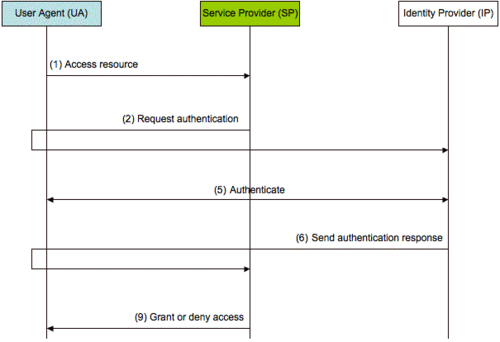
Web-based Single Sign-On and the Dangers of SAML XML Parsing
Security Assertion Markup Language \(SAML\) is a popular XML-based open standard for exchanging authentication and authorization data between two systems.
Perfect Forward Secrecy and more…
Last month we started rolling out some subtle changes to SendSafely that many users may not have noticed.