
Most Sovereign AI discussions focus on models, where they run and who can access prompts. But the bigger risk sits upstream in the data pipeline. By the time customer data reaches your sovereign AI, it has already passed through chat tools, ticketing systems, and SaaS platforms that may store, index, or reuse it. In some cases, it may even have been used to improve someone else’s AI product. We’ve written about this before in “Your customers’ sensitive PII shouldn’t be training someone else’s AI.”
This post explores how SendSafely enables a truly sovereign data pipeline. SendSafely acts as the trust layer beneath your AI powered customer service stack, ensuring sensitive customer data is protected from the moment it’s submitted through processing and delivery. It is the encrypted data infrastructure your sovereign data pipeline relies on. And the good news is: you can add this trust layer without replacing your helpdesk, without a major engineering project, and without asking your customers to do anything complicated.
What a Sovereign Data Pipeline Actually Looks Like
The architecture we’re describing is straightforward:
1. Sensitive data never touches your vendor platforms in the clear. It arrives encrypted through SendSafely, gets processed by your own secure infrastructure, and only a reference to encrypted content flows into Salesforce, Zendesk, or wherever your agents work.
2. All processing, including by AI, happens in an environment you control. Using services like AWS Bedrock, you can access frontier models without exposing your data to model providers or allowing it to be retained or used for training.
SendSafely sits at the foundation of this architecture, as the encrypted data trust layer providing encrypted storage, controlled access, and a programmable data flow via SendSafely Actions. Above it sits your processing layer: e.g. your Bedrock instance, AV scanning, and file validation. Further up, your applications, such as CRM and AI Chat agents sit, interacting only with metadata, never raw sensitive content.
The result is a genuinely sovereign pipeline: data is encrypted at intake, processed within your environment, and securely delivered, without third-party platforms ever accessing the underlying content.
Here’s how the workflow plays out in practice.
The Sovereign Data Pipeline: Step by Step
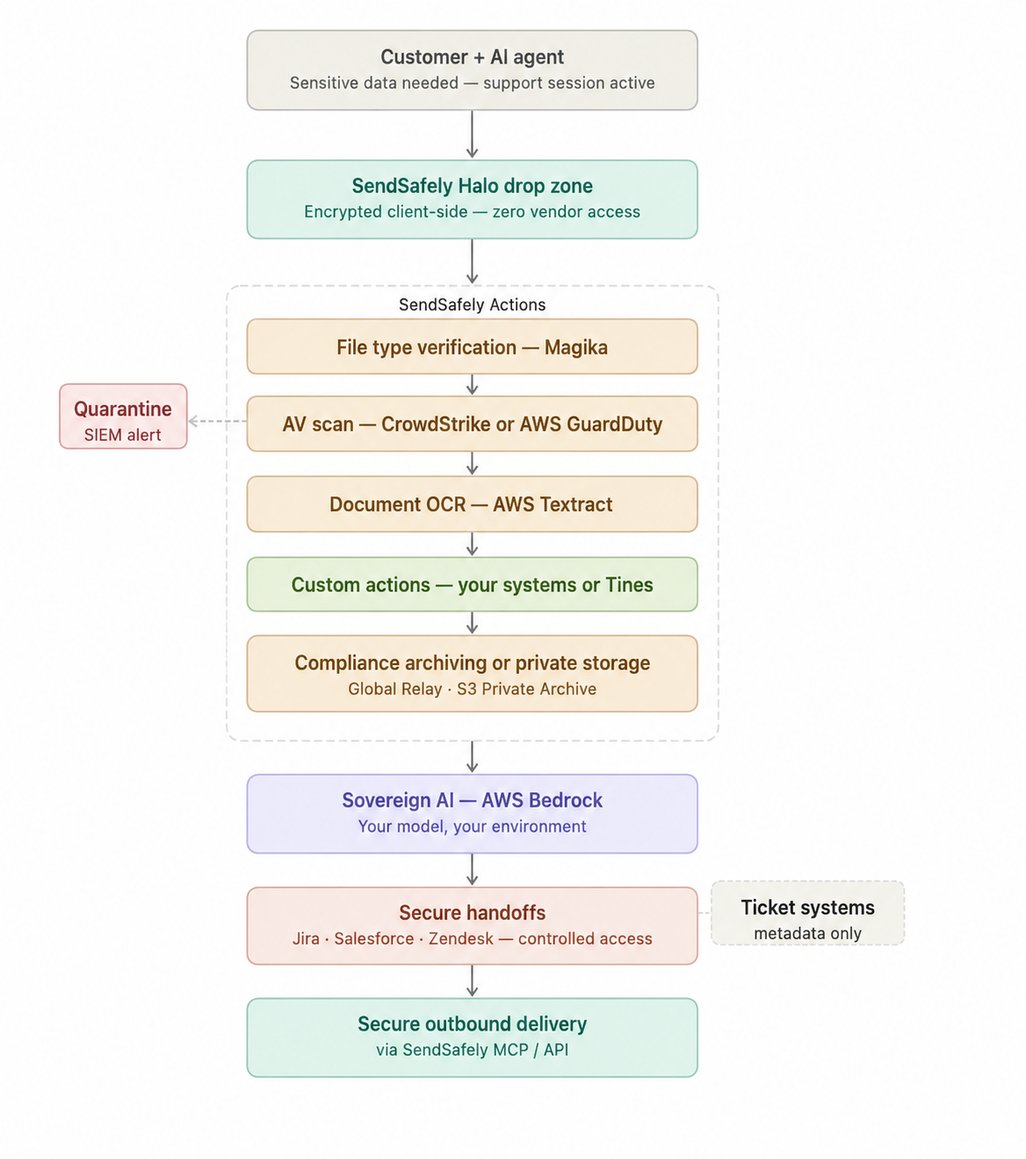
Step 1: Secure Intake (HALO)
Your AI chat agent is working through a customer’s issue. Maybe it’s a KYC check that requires a passport scan or a platform bug requiring a HAR file. The moment your agent determines sensitive files are needed, it’s trained to present a SendSafely HALO dropzone to securely collect the data.
HALO is the encrypted intake at the start of the pipeline — an end-to-end encrypted file upload purpose-built for AI support workflows. The file lands in SendSafely, protected and under your control, before any other system in your stack touches it.
Step 2: Controlled Processing in your own environment (Actions)
Once the file is submitted, SendSafely Actions are the event-driven automation layer that triggers processing steps inside your environment. With Actions, you can decrypt and process files while keeping the decrypted content entirely within your control boundary.
Actions connect SendSafely, as your encrypted data trust layer, to the rest of your infrastructure. You’re not delegating processing to a third party, you’re using your own tools, such as your AV scanner, compliance tooling, or OCR, to operate on files that never leave your encrypted perimeter.
Here’s what that Actions pipeline could look like in sequence within the secure perimeter of an AWS environment:
- File Type Verification - Magika
The first Action verifies the file is what it claims to be using Magika. It analyzes file content, not just extensions to prevent spoofed files (like executables renamed as PDFs) from slipping through. Questionable files are quarantined or rejected.
- Anti-Virus Scanning — Your Scanner, Your Rules
With file type confirmed, the next Action invokes your existing AV infrastructure, for example AWS S3 AV Scanning with GuardDuty. Clean files continue. Infected files are quarantined, removed, and trigger alerts through your standard SIEM workflow. You can also integrate trusted external platforms such as CrowdStrike, Opswat, or Sophos via Actions if you already utilize them for your endpoint protection.
- Document Intelligence — AWS Textract OCR
Once a file is validated, an AWS Textract Action extracts structured data from documents such as passports, bank statements, onboarding forms. This turns files into queryable content your AI can use directly, all within your AWS environment.
- Custom Actions — Your Systems, Your Logic
Not every workflow fits a pre-built action, and SendSafely makes it straightforward to build your own. A Custom Action is simply a webhook or Lambda call that SendSafely triggers at the right moment in your workflow and from there, you own the logic entirely. That might mean handing off to an internal document processing service, calling a proprietary fraud detection model, enriching data against an internal customer database, or routing metadata to a trusted SaaS automation platform like Tines for orchestration.
- Compliance Archiving — S3
For organizations operating in regulated industries, the SendSafely Global Relay Action is designed to meet compliance requirements. Alternatively, the S3 Private Archive Action can concurrently write a copy of the file directly to a private WORM compliant S3 bucket within the enterprises own AWS environment.
Step 3: Sovereign AI Processing — Your Model, Your Environment
Files that pass validation move to AI processing within your environment.
Instead of sending data to third-party AI services - Actions can hand it off to AWS Bedrock, where models such as Anthropic Claude, Llama, Mistral, and others run without visibility into your inputs or outputs and without retaining your data.
Bedrock processes the content according to your use case, e.g. generating summaries, a customer specific response, or triggering downstream case management logic entirely within your sovereign environment. Processing outputs are posted back to CRM cases or support desk tickets, and if those outputs contain sensitive data, they too can be encrypted with SendSafely.
This combination, SendSafely for encrypted data handling and AWS Bedrock for sovereign AI processing is what makes the pipeline truly sovereign.
Step 4: Secure Handoffs — Only Who (or What) Needs to Know
Not every support case gets resolved in a single chat session by a single AI agent. Complex issues get escalated. Platform bugs get routed to engineering. Compliance matters get handed to Trust and Safety. Without a sovereign data pipeline, every handoff point means more people with access, more platforms holding copies.
SendSafely makes that handoff chain secure. You control exactly who (or what) can see a file at any point in its lifecycle, and you can change that access list instantly as the case evolves.
Take the engineering escalation scenario: a customer’s HAR file needs to be shared with your engineering team in Jira. Your pipeline creates a Jira issue and inserts a SendSafely package link. It then grants access only to the relevant engineers. They view the HAR file from the secure link, no copying files, no attachments. When the Jira ticket is resolved and closed, access is revoked. The file never lives in Jira — it lives in SendSafely, where you control it. This means the HAR file itself is never exposed to Atlassian’s own AI.
Step 5: Secure Outbound Delivery — the Loop Closed
If the resolution of the customer’s issue requires sending back something sensitive — a signed document, a verification result, account details — the same principle applies in reverse. Your pipeline calls SendSafely’s MCP server or API to generate a secure package for the customer. The sensitive content goes out through SendSafely’s end-to-end encrypted delivery, not through email or a plain attachment.
The customer receives a secure link. The content stays protected. The loop is closed.
Sovereign AI Requires Sovereign Data Infrastructure
Most AI sovereignty conversations focus on the model, where it runs and what it can access. But sovereignty only holds if it extends upstream. A sovereign model fed pre-exposed data isn’t sovereign, it’s just a different point of leakage.
SendSafely closes that gap. It provides the encrypted data layer beneath your pipeline, ensuring sensitive data is protected at intake, during processing, and in delivery.
HALO secures intake. Actions handle processing within your environment. Access controls enforce least-privilege at every handoff. SendSafely’s API ensures data is delivered as securely as it arrived.
Your tools don’t change. Your workflows don’t change. What changes is the layer underneath, the one that protects the data.
Your customers trust you with their most sensitive information. This is how you keep it that way.
Ready to build your sovereign support pipeline?__ Learn more about SendSafely HALO and __ explore the SendSafely Actions Library.
SendSafely: Integrated File Transfer for the Apps you Love
If you are looking for a secure way to transfer files with customers or business partners, our platform might be right for you. Contact us today to request a demo and free trial subscription.
Request a Demo


